About This Tool
How this tool breaks a number down into its prime factors using trial division
Every whole number greater than 1 can be built from prime numbers multiplied together in exactly one way, ignoring order. That statement is the Fundamental Theorem of Arithmetic, and it is why prime factorization is not just a puzzle, it is a unique fingerprint for every integer. This tool finds that fingerprint using trial division, the most direct method there is: testing whether small primes divide evenly into the number, and dividing them out when they do.
The whole process runs client side with exact integer arithmetic, and it is capped at numbers up to 10 to the power 12, one trillion, which keeps even the worst case, a large prime near that ceiling, resolving in well under a second in the browser.
The trial division algorithm
Step 1 Strip out all factors of 2 first
2 is handled as a special case before the main loop, dividing it out repeatedly until the number is odd. This immediately halves the search space for every other step, since no even number past this point needs checking.
Step 2 Test only odd candidates
Starting from 3, the tool tries only odd numbers as potential factors, skipping every even candidate since they were already eliminated in step 1.
Step 3 Stop at the square root of what remains
The loop only needs to test candidates up to the square root of the remaining value, not the original number. If no factor exists at or below that square root, whatever remains must itself be prime, since any composite number has at least one factor at or below its own square root.
Step 4 Recompute the limit as the remainder shrinks
Each time a factor is found and divided out, the square root limit is recalculated against the smaller remaining value, so the search window keeps shrinking as the algorithm progresses rather than staying fixed to the original number.
// trial division: strip 2s, then test odd candidates up to sqrt
take(2);
for (var p = 3; p * p <= rem; p += 2) take(p);
if (rem > 1) factors.push({ p: rem, e: 1 });
Every number up to one trillion fits exactly in a JavaScript number, which is exact for whole numbers up to about 9 quadrillion. So instead of taking a square root, the loop simply checks p × p against what remains. That comparison is exact, with no floating point rounding creeping into a decision about whether a candidate factor is above or below the limit.
| Number | Factorization | Distinct primes |
|---|
| 360 | 2³ × 3² × 5 | 3 |
| 97 | 97 (prime) | 1 |
| 1024 | 2¹&sup0; | 1 |
| 1001 | 7 × 11 × 13 | 3 |
Worked example: 360. Dividing out 2s three times leaves 45 (360 ÷ 8). 45 is odd, so the odd-candidate loop begins at 3, which divides in twice, leaving 5 (45 ÷ 9). At that point the square root of 5 is under 3, so the loop stops, and the remaining value, 5, is added directly as a prime factor. Final result: 360 = 2³ × 3² × 5. Multiply it back out yourself: 8 × 9 × 5 = 360, confirming the factorization is exact, not approximate.
Special cases handled explicitly
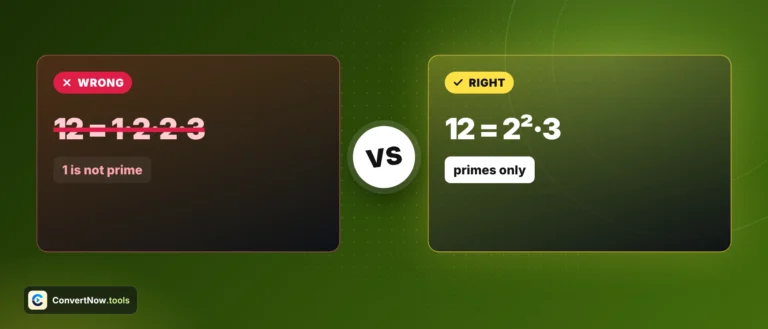
0 has no factorization since every number would divide it, and 1 is neither prime nor composite, it is the empty product. Both are called out directly rather than left to produce a confusing blank result.
Exponent notation
Repeated factors are shown with superscript exponents, like 2³, and the result also reports the total factor count both by distinct primes and counted with multiplicity.
Trial division up to sqrt(n)
Exact BigInt arithmetic
Supported up to 10^12
What factorisation is good for
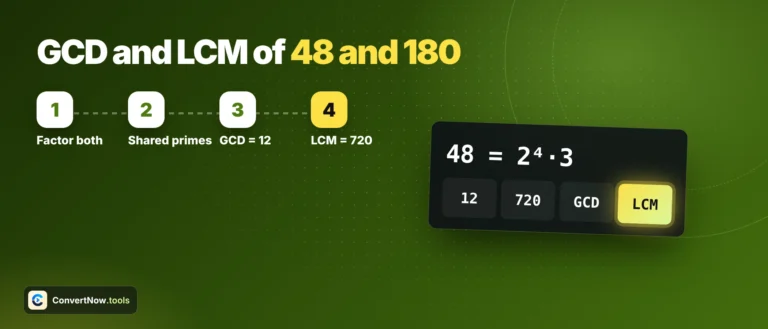
Simplifying fractions and radicals in algebra homework, finding the greatest common divisor or least common multiple by comparing prime factorizations directly, checking whether a number is prime before using it in a hashing or modular arithmetic context, and teaching the building block concept behind cryptographic systems that rely on factoring being computationally hard for very large numbers, even though this tool's 10^12 ceiling is nowhere near cryptographic scale. Any time you need to see what a number is actually made of, rather than just what it equals, this is the operation for it.