
How Do Hackers Crack Passwords? Real Methods Explained
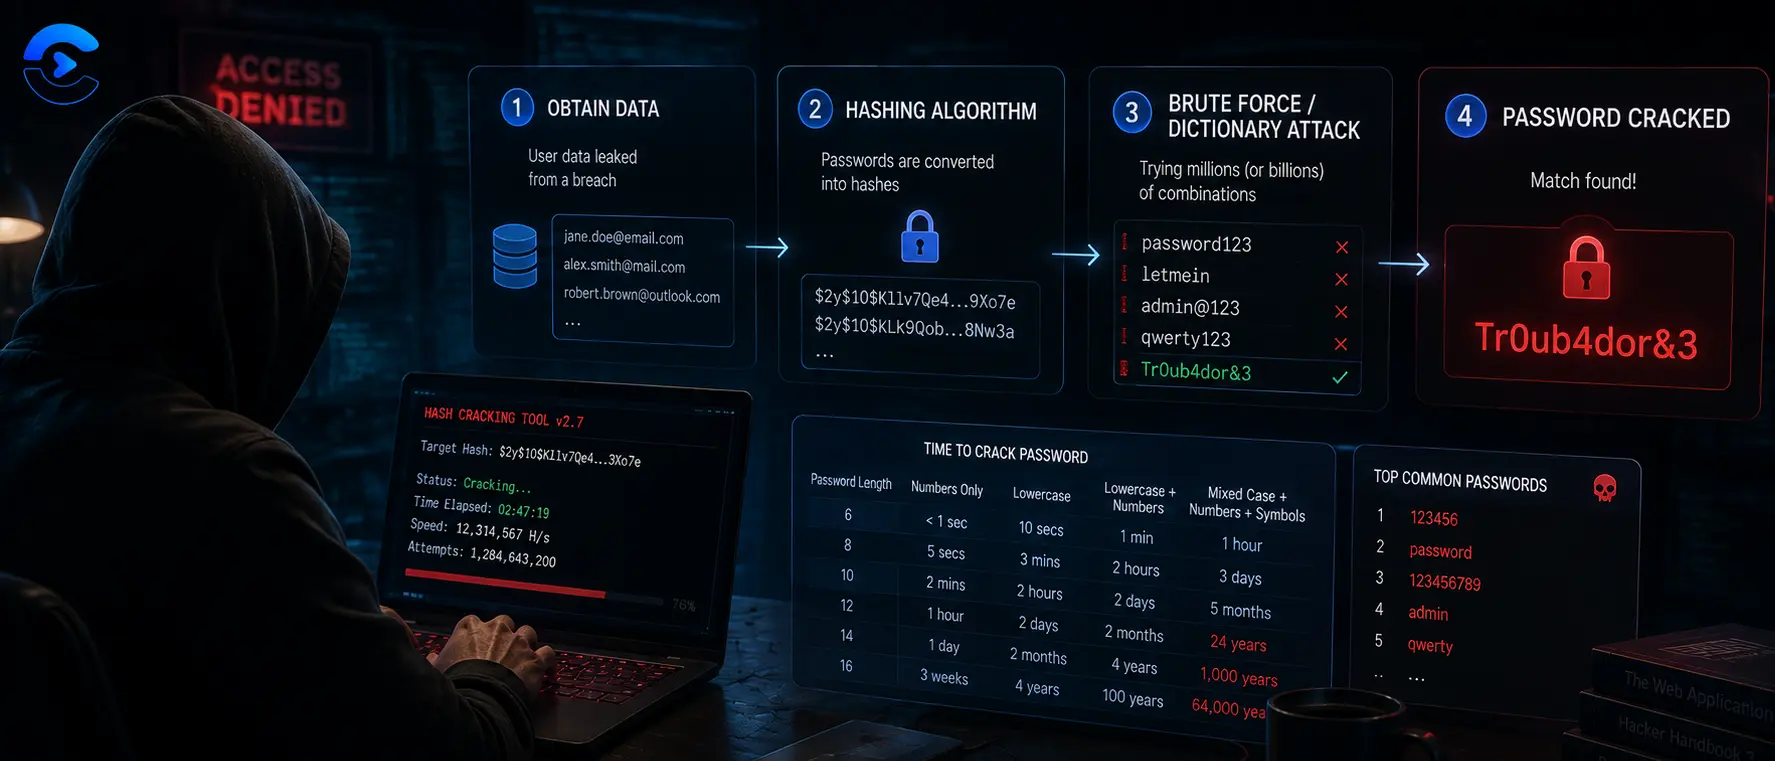
How do hackers crack passwords in practice? Mostly they do not guess one character at a time in front of a login box. They steal a database of password hashes, then run that file through cracking software on their own hardware, testing millions or billions of guesses per second using leaked password lists, common word patterns, and raw brute force. The account holder never sees a single failed login attempt, because the attack never touches the real service at all. Length, randomness, and unique passwords per site are what make this process take years instead of minutes.
The two workhorse methods: dictionary and brute force
Almost every password cracking method is a variation on two ideas. A dictionary attack tests real words, common phrases, and known leaked passwords first, because people reuse the same handful of patterns constantly. A brute force attack tests every possible combination of characters, starting short and working upward, with no assumptions about what a human would pick.
Dictionary attacks are fast against weak passwords because they skip straight to the likely answers. Cracking tools ship with lists containing hundreds of millions of real passwords pulled from past data breaches, plus rules that automatically try common tweaks like adding a number at the end or swapping a letter for a symbol.
Brute force is the fallback when the dictionary comes up empty. It is slower, but modern graphics cards make it far less slow than most people assume. A weak, short password can fall in seconds. A long, random one can take longer than the attacker has patience for, sometimes centuries at current hardware speeds.
How do hackers crack passwords offline
This is the part that surprises most people about how hackers crack passwords: the attack usually happens far away from the login page. When a company gets breached, attackers often walk away with a database of password hashes rather than plain text passwords. A hash is a one way scrambled version of the password, and services are supposed to store only the hash, never the original.
Once that hash database is in hand, the attacker takes it offline and cracks it on their own machines, with no rate limits, no lockouts, and no one watching. They can try billions of guesses per second on specialized hardware, hashing each guess and comparing it against the stolen file. Weak hashing algorithms make this dramatically faster, which is why security standards bodies like NIST recommend slow, purpose built hashing functions for storing passwords rather than fast general purpose ones. You can read the details in the NIST digital identity guidelines.
Rainbow tables and precomputed guesses
A rainbow table is a precomputed set of hash values mapped back to the passwords that produced them. Instead of hashing every guess in real time, an attacker looks the hash up in a table that was built once and reused across many targets. Modern systems defend against this by adding a random value, called a salt, to each password before hashing it, which forces attackers back to slower per account cracking.
Credential stuffing: reusing what already leaked
A huge share of real world account takeovers do not involve cracking anything new at all. Attackers take usernames and passwords from one breach and simply try them against other sites, betting that people reused the same password somewhere else. This is called credential stuffing, and it works often enough to remain one of the most common attack types in use today.
The defense here has nothing to do with password complexity. It comes down to never reusing a password across sites, so that one leaked account cannot open every other account tied to the same email address.
What actually slows an attacker down
Length beats complexity almost every time. A fourteen character passphrase built from unrelated words resists both dictionary and brute force attacks far better than a shorter password stuffed with symbols in predictable spots, because total length is what drives up the number of possible combinations an attacker has to test.
Uniqueness matters just as much. A strong password reused across ten accounts is only as safe as the weakest of those ten services. Pair a password manager with a habit of checking new passwords before you commit to them, and most of these attack methods lose their edge entirely.
Security checks you can run now
Once you know how hackers crack passwords, the next step is closing the gaps they rely on. A password generator creates long, random passwords that resist both dictionary and brute force attacks from the start. If you manage a website, a SSL certificate checker confirms your login pages are actually encrypted in transit, and an HTTP header checker flags missing security headers that make attacks easier. Curious who is behind a domain sending suspicious login requests? A DNS lookup tool can help trace it. Browse the rest of the tools library or check the ConvertNow blog for more security explainers like this one.
Check your password before an attacker does
Most people cannot tell the difference between a password that takes minutes to crack and one that takes centuries, until it is too late. Our free Password Strength Checker scores your password instantly against real cracking patterns, so you know exactly how it holds up before you use it anywhere.
Open the Password Strength CheckerHow to stay ahead of crackers
Hackers rarely sit at a login screen guessing passwords one by one. They steal hashed password databases and crack them offline using dictionary lists, brute force, and precomputed tables, then reuse any leaked credentials against other sites through credential stuffing. Length and uniqueness are what make each of these methods slow and expensive instead of fast and free. Run any password you are about to use through the Password Strength Checker above and give attackers nothing easy to work with.
How do hackers crack passwords? The math behind the time estimates
The main post covers the methods behind how do hackers crack passwords. This section puts numbers on them. Whenever someone asks how do hackers crack passwords, the honest answer is a division problem: possible passwords divided by guesses per second. Every figure below assumes 10 billion guesses per second. That is an assumption for a fast, unsalted hash on a multi GPU rig, not a measured rate for any one system.
| Case for the how do hackers crack passwords question | Possible combinations | Time to try all at 10 billion per second |
|---|---|---|
| Case 1 for how do hackers crack passwords: 8 random lowercase letters | 208,827,064,576 | 20.9 seconds |
| Case 2 for how do hackers crack passwords: 8 random characters from 95 printable | 6,634,204,312,890,625 | 7.7 days |
| Case 3 for how do hackers crack passwords: 12 random characters from 95 printable | about 5.4 x 10^23 | 1.7 million years |
| Case 4 for how do hackers crack passwords: 4 random words from a 7,776 word list | 3,656,158,440,062,976 | 4.2 days |
| Case 5 for how do hackers crack passwords: 6 random words from a 7,776 word list | about 2.2 x 10^23 | 701,021 years |
Those times are for trying every option. On average a cracker finds the answer after half of them. The table answers how do hackers crack passwords for each case and shows why length beats complexity. Going from 8 to 12 random characters multiplies the work by 95 four times over, roughly 81 million.
How do hackers crack passwords faster than the raw math suggests?
That is the real answer to how do hackers crack passwords at speed: they skip the raw math whenever they can. A rule based attack takes a list of 1 million common words, tries each with and without a capital letter, adds a two digit or four digit year ending, then a symbol. The sum is 1,000,000 x 2 x 100 x 10 = 2,000,000,000 guesses. At 10 billion per second the whole set takes 0.2 seconds.
A password like Summer2024! looks strong to a form that counts character types. To the cracker it is one tiny corner of the search. This gap explains how do hackers crack passwords so quickly on real leaks. It is the gap between a password that looks complicated and one that actually is.
How do hackers crack passwords when the hash is deliberately slow?
Slow hashing is the best defense a site controls against how do hackers crack passwords. Algorithms such as bcrypt, scrypt and Argon2 are built to burn time and memory on every guess, so the rate falls by several orders of magnitude compared with a plain fast hash. Suppose the rate drops to 10,000 guesses per second. The 8 character random password from 95 symbols then needs about 21,037 years instead of days.
Nobody outside a company can see which hash it uses, so how do hackers crack passwords on that site stays out of your control. Unique passwords are your answer.
Is how do hackers crack passwords different for online logins?
Yes. The online version of how do hackers crack passwords is slower by design. An online attack must go through the login page, so rate limits, lockouts and alerts apply. In how do hackers crack passwords online, even a few guesses per second is a tiny fraction of an offline rate. Attackers adapt with password spraying: one very common password tried against thousands of accounts, a few at a time, so no single account locks. Multi factor sign in stops most of this, because a correct guess alone no longer opens the door.
| Setting for the how do hackers crack passwords question | Typical guess rate | What defends you |
|---|---|---|
| How do hackers crack passwords offline against a fast hash | Billions per second | Length and randomness |
| How do hackers crack passwords offline against a slow hash | Thousands per second | Length plus a good site |
| How do hackers crack passwords through an online login page | A handful per second | Lockouts and multi factor sign in |
A checklist drawn from how do hackers crack passwords in practice
- Make length your first lever. The answer to how do hackers crack passwords always starts with search size, so aim for 16 or more characters on accounts that matter.
- Use a random generator. A human pattern shrinks the search space, and that is exactly what a cracker counts on.
- Keep one unique password per site. Knowing how do hackers crack passwords from old leaks shows why reuse is the weak point.
- Turn on multi factor sign in wherever it is offered, since it blunts every method behind how do hackers crack passwords online.
- Test a candidate with the password strength checker and create new ones with the password generator.
Once you see how do hackers crack passwords as arithmetic, the advice stops sounding like a lecture. Ask how do hackers crack passwords again after each change you make, and the numbers will tell you if it helped. Each extra random character is a multiplier, and each reused password is a shortcut handed to the attacker.
| In this guide |
|---|
| The two workhorse methods: dictionary and brute force |
| Credential stuffing: reusing what already leaked |
| What actually slows an attacker down |
| Security checks you can run now |
| How to stay ahead of crackers |
Mostly they do not guess one character at a time in front of a login box.
FAQ: How Do Hackers Crack Passwords? Real Methods Explained
How do hackers crack passwords without triggering a lockout?
They usually crack a stolen database of password hashes offline, on their own hardware, rather than typing guesses into the real login page. Since the guesses never touch the actual service, there is no lockout or alert to trigger.
What is a dictionary attack?
A dictionary attack tests real words, common phrases, and previously leaked passwords instead of random character combinations, because people tend to reuse the same predictable patterns.
What is a brute force attack?
A brute force attack tries every possible combination of characters in order, starting with short combinations and working up, with no assumptions about what a real password might look like.
Why is offline password cracking more dangerous than online guessing?
Offline cracking has no rate limits and no account lockouts, so attackers can test billions of guesses per second on specialized hardware without anyone noticing until the damage is already done.
What is a rainbow table?
A rainbow table is a precomputed list of hash values matched to the passwords that created them, letting an attacker look up a hash instead of calculating it fresh. Salting each password before hashing defeats this method.
What is credential stuffing?
Credential stuffing is reusing a username and password from one data breach to try logging into other, unrelated sites, betting that the account holder reused the same password more than once.
Does password length matter more than symbols and numbers?
Yes, in most cases. A longer passphrase made of unrelated words creates far more possible combinations than a short password with a few symbols swapped in, which makes length the stronger defense overall.
How long does it take to crack a weak password?
A short, common password can fall in seconds on modern cracking hardware, especially if it appears in leaked password lists. A long, random password can take far longer than an attacker is willing to wait.
Can a strong password still be compromised?
Yes, if it is reused across multiple sites. One breach at any of those sites exposes the password everywhere else it was used, regardless of how strong it was originally.