
How Password Strength Is Measured (And Why It Matters)
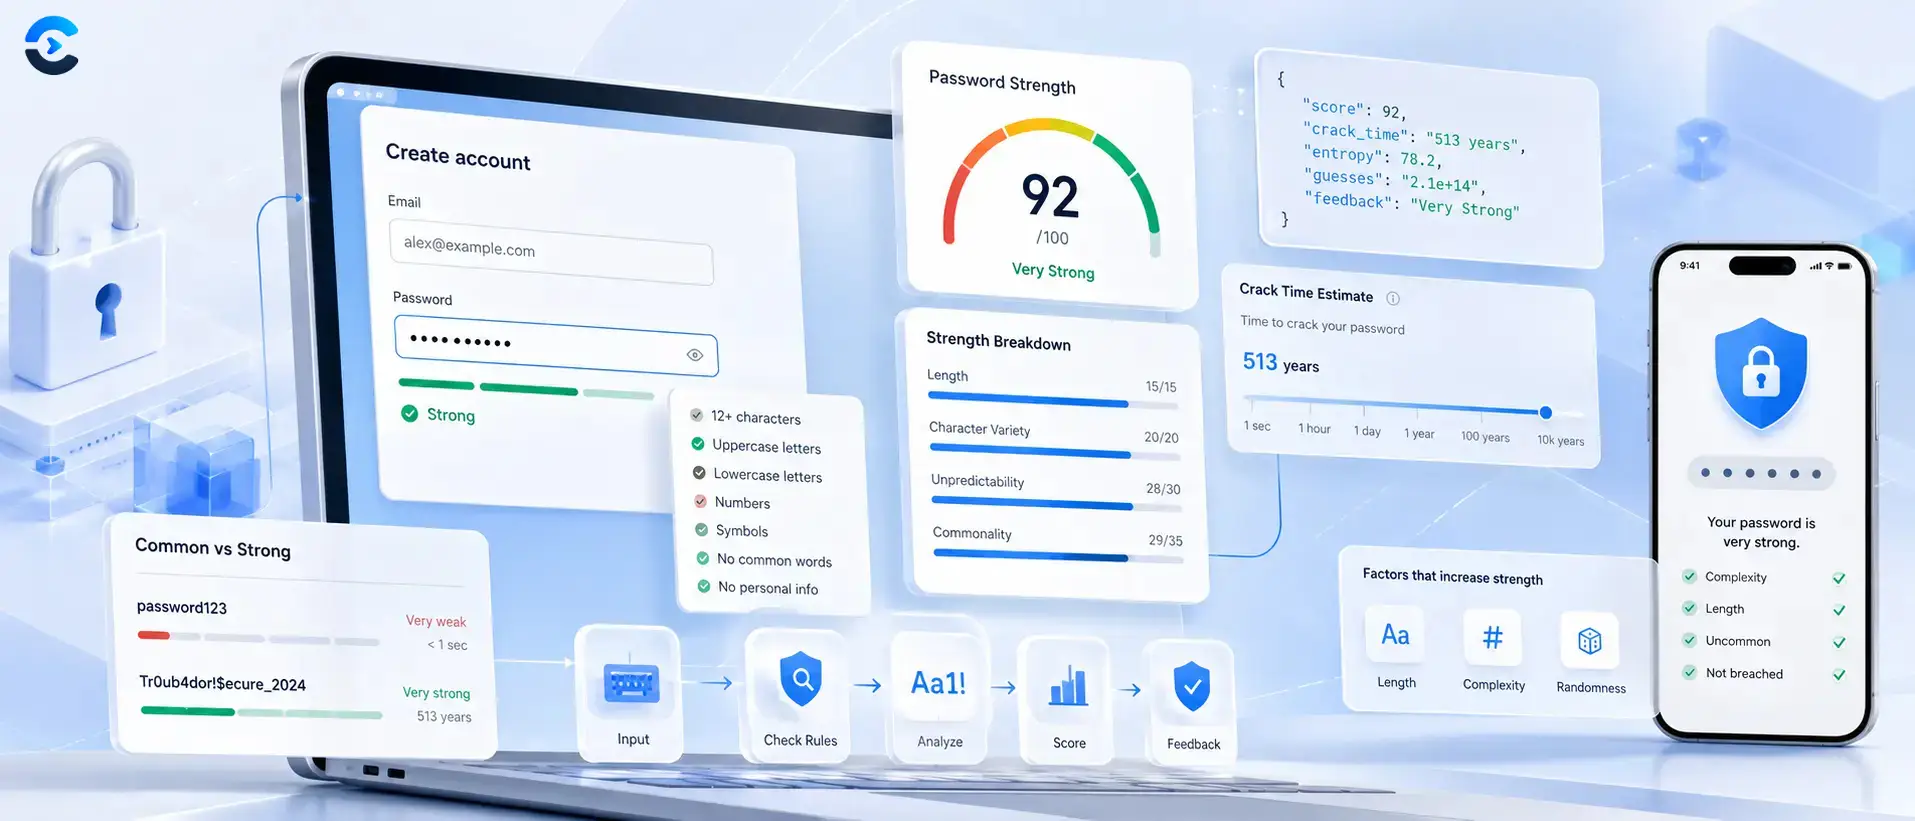
Password strength is measured by combining four factors: length, character set variety, entropy (how many guesses an attacker would statistically need), and pattern detection that flags predictable substitutions and dictionary words. A strength meter is not just counting characters. It is estimating how long a real cracking tool would take to guess your password, which is why a short password full of symbols can score worse than a long plain sentence.
The four factors behind how password strength is measured
Most strength meters, from browser prompts to standalone checkers, blend a small set of signals into one score. None of them look at "complexity" the way people imagine. Here is what they actually check.
1. Length
Length is the single strongest factor. Every extra character multiplies the number of possible combinations an attacker has to try. A 16 character password is dramatically harder to brute force than a 9 character one, even if the shorter one has more symbol variety. This is why security guidance shifted years ago from "use weird characters" to "make it longer."
2. Character set variety
A meter checks whether your password draws from multiple pools: lowercase letters, uppercase letters, numbers, and symbols. Using more pools increases the theoretical guess space per character. But this factor is weaker than most people assume, because variety alone does not stop an attacker who already expects people to swap "a" for "@" or add "1" at the end.
3. Entropy: the real measure of guesswork
Entropy is the core idea behind how password strength is measured, and it sounds more complicated than it is. In plain terms, entropy estimates how many attempts a computer would need to guess your password if it were trying every realistic possibility. Higher entropy means more attempts, which means more time. A password with low entropy might fall in seconds. One with high entropy could take longer than a human lifetime on the same hardware, even without heavy math to explain why.
Entropy is not just about character pool size. It also depends on unpredictability. A password built from random words, random casing, or a passphrase you invented has high entropy because there is no shortcut for a guessing tool. A password built from a common word plus a predictable substitution has much lower real world entropy, no matter how "complex" it looks on screen.
4. Pattern and dictionary detection
This is the factor that surprises people most. Strength meters run your password against lists of common passwords, dictionary words, keyboard patterns like "qwerty", and known substitution tricks such as "@" for "a" or "0" for "o". Attackers use these exact lists first, because most people reuse the same handful of tricks. A meter that skips this check will overrate passwords that a real attacker would crack in the first few minutes.
Password strength is measured by combining four factors: length, character set variety, entropy (how many guesses an attacker would statistically need), and pattern detection that flags predictable substitutions and dictionary words. A strength meter is not just counting characters.
Why P@ssw0rd1 scores lower than a long random passphrase
This is the clearest way to see entropy versus perceived complexity in action. "P@ssw0rd1" looks strong at a glance. It has uppercase, lowercase, a symbol, and a number. But it is built from a single dictionary word with substitutions that cracking tools check automatically. A long passphrase made of unrelated words looks plain by comparison, yet it holds up far better because there is no pattern to exploit and the sheer length multiplies the guess space.
| Password | Looks like | Real strength | Why |
|---|---|---|---|
P@ssw0rd1 |
Complex, mixed characters | Weak | Based on a common word with predictable substitutions that cracking tools check first |
correct horse battery staple style |
Plain lowercase words | Strong | Long, unrelated words with no common pattern, giving it far more real guess space |
Check your own password against these factors
Reading about entropy and pattern detection is one thing. Seeing your own password scored against them is more useful. The Password Strength Checker breaks down length, character variety, estimated entropy, and common pattern matches in real time, right in your browser, so you can see exactly why a password scores the way it does before you use it anywhere.
What actually makes a password hard to crack
Combine the four factors instead of maximizing just one. Aim for length first, at least twelve to sixteen characters. Mix in variety where it is easy to remember rather than forced. Avoid whole words tied to you, your pets, or your birthday, since those are the first guesses in any dictionary attack. Most importantly, do not rely on visual complexity as a stand in for real unpredictability.
If you also manage passwords for accounts across a team or family, generating fresh random passwords with a password generator removes the guesswork entirely, since you are not relying on your own pattern habits at all.
Password strength is one piece of a bigger security habit. If you are storing or transmitting sensitive values and need a one way check instead of a reversible password, a hash generator covers that separate use case. For a broader set of security utilities, the security tools hub lists everything in one place, and the ConvertNow blog has more explainers like this one.
What makes a password strong, in short
How password strength is measured comes down to length, variety, entropy, and whether your password matches a known pattern attackers already check first. A long unpredictable phrase will almost always beat a short password dressed up with symbols. Run your next password through the Password Strength Checker before you commit to it, and lean on a generator when you want a fresh one with no guesswork involved.
How Password Strength Is Measured in Numbers: Entropy Worked Out Step by Step
The main guide names the four factors. Now let us do the arithmetic, because how password strength is measured becomes clear once you see the bits. Entropy in bits equals the length times the base 2 logarithm of the pool size. Every extra bit doubles the guesses needed.
How password strength is measured for random strings of different length
Take a few random passwords and run the formula to see how password strength is measured. For the time column we assume an attacker with a stolen fast hash list who tries 10 billion guesses per second, and finds the answer on average after trying half the space. That rate is an assumption for illustration, not a promise about any real system.
| Password type and how password strength is measured | Bits of entropy | Average time at 10 billion a second |
|---|---|---|
| 8 random lowercase letters (how password strength is measured: weak) | 37.6 | About 10 seconds |
| 8 random characters from 95 printable (how password strength is measured: better) | 52.6 | About 3.8 days |
| 12 random lowercase letters and digits (how password strength is measured: moderate) | 62.0 | About 7.5 years |
| 16 random lowercase letters (how password strength is measured: strong) | 75.2 | About 69 thousand years |
| 12 random characters from 95 printable (how password strength is measured: very strong) | 78.8 | About 856 thousand years |
Look at row 4 against row 2 to see how password strength is measured at work. A longer all lowercase string beats a shorter one with symbols by a huge margin. That is the core of how password strength is measured: length wins.
How password strength is measured for passphrases
Here is how password strength is measured for a passphrase. It picks words at random from a list. The popular Diceware list holds 7776 words, so each word adds log2 of 7776, about 12.9 bits. Six words give 77.5 bits, close to the 12 character mixed password above, and many people find them easier to remember.
| Random words, how password strength is measured | Bits | Average time at 10 billion a second |
|---|---|---|
| 4 words (how password strength is measured for short phrases) | 51.7 | About 2.1 days |
| 5 words (how password strength is measured: good) | 64.6 | About 45 years |
| 6 words (how password strength is measured: very strong) | 77.5 | About 350 thousand years |
The word random is doing all the work here. A phrase from a song or a quote is not random, and a meter that checks patterns will score it far below these figures.
Online versus offline
These times describe an offline attack against a stolen list of hashes. A website with rate limits allows only a few guesses a minute, so the same password lasts far longer there. Slow hashes such as bcrypt cut the guess rate by orders of magnitude too. How password strength is measured depends on the threat you picture.
Why does how password strength is measured differ between meters?
Two meters can disagree on the same password, because how password strength is measured is not standardized. One may count only length and character types. Another, such as zxcvbn style estimators, also looks up words, names, dates and keyboard walks, and then charges only a few bits for each pattern it finds. That second kind comes closer to how password strength is measured by a real cracking tool.
- A basic meter reports the maximum possible entropy, so how password strength is measured is shallow.
- A pattern aware meter reports the likely entropy, so how password strength is measured is more honest.
- A good meter explains its score and shows how password strength is measured, so you can fix the weak part.
- No meter can see whether you reused the password on another site.
The last point matters most. Reuse turns a strong password into a weak account, since one leak exposes every login that shares it. Even the best answer to how password strength is measured cannot catch that.
So use the numbers as a guide. As a rule of thumb, aim for around 70 bits on important accounts, keep each password unique, and turn on a second factor. When you ask how password strength is measured, remember the formula, the guess rate, and the pattern checks.
| In this guide |
|---|
| The four factors behind how password strength is measured |
| Why P@ssw0rd1 scores lower than a long random passphrase |
| What actually makes a password hard to crack |
| What makes a password strong, in short |
FAQ: How password strength is measured?
How is password strength measured exactly?
Strength meters combine length, character set variety, an entropy estimate of how many guesses an attacker would need, and a check against common patterns and dictionary words. The final score weighs all four rather than any single factor alone.
Is a longer password always stronger than a shorter one with symbols?
In most cases yes, because length multiplies the total guess space more than adding a symbol or two does. A short password with symbols can still be weak if it is based on a common word or pattern.
What is password entropy in simple terms?
Entropy is an estimate of how many attempts a computer would need to guess your password by trying realistic possibilities. Higher entropy means more attempts and more time required, which makes the password harder to crack.
Why does P@ssw0rd1 score as weak?
It is built from the common word "password" with substitutions that cracking tools already check for by default, such as swapping "a" for "@" and "o" for "0". The visual complexity does not add real unpredictability.
Are passphrases better than traditional passwords?
Yes, in most cases a passphrase of several unrelated words is both easier to remember and harder to crack than a short password packed with symbols, because the length and unpredictability raise the entropy significantly.
Does adding numbers to the end of a word make it strong?
Not by much. Appending a number or two to a common word is one of the first patterns cracking tools test, so it adds very little real protection even though it changes how the password looks.
How many characters should a strong password have?
Twelve characters is a reasonable minimum today, and sixteen or more is safer, especially if you use a passphrase style. Length matters more than any single character type you add.
What is a dictionary attack?
A dictionary attack tries common words, known passwords, and predictable variations of them before attempting random guesses. It succeeds quickly against passwords based on real words, even with substitutions applied.
Can I check my password strength without saving it anywhere?
Yes, tools like the Password Strength Checker run the calculation in your browser, so you can test a password and see its length, variety, entropy, and pattern score without sending it anywhere.
Sources and further reading
- NIST SP 800-63B: the US federal guidance on passwords and length.
- Password strength on Wikipedia: entropy math in more depth.